
SECTION 1
Historical Context & Motivation
The Internet did not emerge from a single invention but rather from decades of research into distributed communication systems that could survive partial failures. During the Cold War, the United States Department of Defense funded research into networks that lacked a single point of failure, because a centralized hub-and-spoke telephone system could be incapacitated by a single strike. The fundamental question driving this research was deceptively simple: how can autonomous computers owned by different organizations exchange data reliably across unreliable physical links? The answer—a layered, packet-switched architecture governed by open standards—became the foundation of the modern Internet and reshaped virtually every domain of human activity.
1969 • ARPANET Goes Online
1983 • TCP/IP Becomes the Standard
1991 • The World Wide Web
2007 • Mobile Internet Explosion
2020s • IoT & Ubiquitous Connectivity
From four university nodes in 1969 to billions of connected devices today, the Internet's growth raises a central question for AP Computer Science Principles: what design decisions allow such a massive, decentralized system to function reliably without any single entity controlling it? Understanding the Internet's architecture—its protocols, addressing schemes, routing strategies, and layers of abstraction—is essential for evaluating the benefits, risks, and societal impacts of our increasingly connected world.
SECTION 2
Core Principles & Definitions
The Internet is built on a small set of powerful design principles that enable scalability, fault tolerance, and openness. These principles distinguish it from earlier centralized communication systems and explain why it has been able to grow exponentially without a master redesign. Understanding these foundations is critical for the AP CSP exam, which emphasizes how the Internet's open, layered architecture affects computing innovation and society at large.
Packet Switching
Open Protocols & Standards
Redundancy & Fault Tolerance
Scalability
Layered Abstraction
KEY TAKEAWAY
SECTION 3
How Packets Travel: A Visual Explanation
The following diagram illustrates the journey of data from a sending device to a receiving device across the Internet. Notice the multiple possible paths between routers—this redundancy is what makes the Internet fault tolerant. When a user sends a message, the data is divided into packets, each of which carries a source IP address, a destination IP address, and a sequence number so that the receiving device can reassemble the message even if packets arrive out of order.
Several critical details emerge from this visualization. First, no single router sees the entire path; each router examines only the destination IP address in the packet header and forwards the packet to the next best hop based on its own routing table. Second, different packets from the same message may take entirely different routes and still arrive at the destination, where they are reordered using sequence numbers. Third, this redundant topology means the loss of a single router or link does not disconnect the network—exactly the fault tolerance the Internet was designed to achieve.
SECTION 4
Protocols & the Layered Architecture
The Internet's functionality is organized into a layered model where each layer handles a specific aspect of communication. The AP CSP framework emphasizes the Internet protocol suite (commonly called TCP/IP), which defines four primary layers. Layering is a form of abstraction: a web developer writing HTML does not need to understand how electrical signals propagate through fiber-optic cable, just as a network engineer configuring routers does not need to know the content of the web pages being transmitted. This separation of concerns enables independent innovation at each layer.
The Four Layers of TCP/IP
| Layer | Purpose | Key Protocols / Examples |
|---|---|---|
| Application | Provides services directly to users and applications (web browsing, email, streaming) | HTTP/HTTPS, SMTP, DNS, FTP |
| Transport | Manages end-to-end communication, breaking data into segments, ensuring reliable or fast delivery | TCP (reliable, ordered) and UDP (fast, no guarantee) |
| Internet | Handles logical addressing and routing of packets across networks | IP (IPv4, IPv6), ICMP |
| Network Access / Link | Governs physical transmission of bits over a specific medium (copper, fiber, wireless) | Ethernet, Wi-Fi (802.11), Bluetooth |
The four layers of the TCP/IP model, from highest abstraction (Application) to lowest (Link)
Key Protocols in Detail
IP (Internet Protocol) is the addressing system that assigns every device a unique logical address. IPv4 addresses are 32 bits long, expressed in dotted-decimal notation (e.g., 192.168.1.5), providing approximately 2³² ≈ 4.3 billion unique addresses. Because this space is nearly exhausted, IPv6 uses 128-bit addresses (e.g., 2001:0db8:85a3::8a2e:0370:7334), offering 2¹²⁸ ≈ 3.4 × 10³⁸ addresses—enough to assign a unique address to every atom on the Earth's surface many times over.
TCP (Transmission Control Protocol) operates at the transport layer and guarantees reliable, ordered delivery by requiring acknowledgments from the receiver. If a packet is lost, TCP retransmits it. In contrast, UDP (User Datagram Protocol) sacrifices reliability for speed—no acknowledgments, no retransmission—making it ideal for real-time applications like video streaming or online gaming where a dropped frame is preferable to a delayed one.
DNS (Domain Name System) translates human-readable domain names (e.g., www.example.com) into IP addresses. DNS functions as a distributed hierarchical database: your device queries a local resolver, which may query root servers, top-level domain servers, and authoritative name servers in succession until the corresponding IP address is found.
HTTP/HTTPS (HyperText Transfer Protocol / Secure) is the application-layer protocol used for web communication. HTTP defines how a client (browser) requests a resource and how a server responds. HTTPS adds a layer of encryption via TLS (Transport Layer Security), protecting data in transit from eavesdropping and tampering. When you see a padlock icon in your browser's address bar, your connection is using HTTPS.
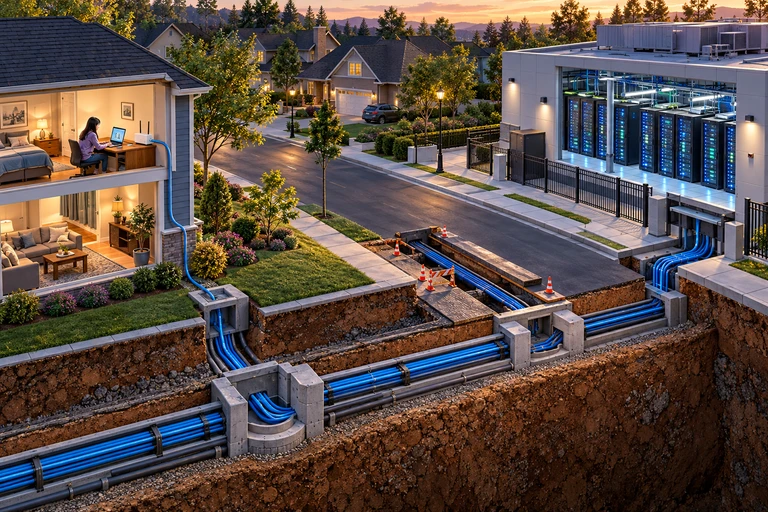 A web request depends on physical cables and equipment as well as protocols. The network-access layer carries bits; IP handles routing, while application protocols define the request and response.
SECTION 5
IP Addressing, DNS, and Routing
Every device on the Internet needs a unique address for packets to find it, just as every house needs a street address for mail delivery. This section examines how IP addressing works, how domain names map to those addresses, and how routers decide which path to forward each packet along.
IPv4 vs. IPv6 Address Space
IPV4 ADDRESS SPACE
Each IPv4 address is 32 bits, written as four octets in decimal (e.g., 172.16.0.1). This space is virtually exhausted.
IPV6 ADDRESS SPACE
Each IPv6 address is 128 bits, written as eight groups of four hexadecimal digits (e.g., 2001:0db8:85a3:0000:0000:8a2e:0370:7334). This provides essentially unlimited addresses for future growth.
Routing is the process by which routers determine the best next hop for each packet. Each router maintains a routing table that maps destination address prefixes to outgoing interfaces. Routers exchange information using routing protocols (such as BGP for inter-domain routing) so that their tables stay current as the network topology changes. Importantly, routing is dynamic: if a link goes down, routers update their tables and packets automatically flow along an alternative path. This dynamic rerouting is the mechanism behind the Internet's fault tolerance.
SECTION 6
Worked Example: Tracing a Web Request
Let us trace exactly what happens, layer by layer, when a user types https://www.example.com/index.html into a browser and presses Enter. This worked example integrates DNS, TCP, IP, HTTP, and encryption into a single coherent narrative.
Tracing a Web Request End-to-End
- 1
Step 1 — DNS Lookup
The browser extracts the domain namewww.example.comfrom the URL. It checks its local cache; if the IP address is not cached, it queries the operating system's DNS resolver, which in turn queries upstream DNS servers (root → .com TLD → authoritative server for example.com).DNS returns the IP address93.184.216.34 - 2
Step 2 — TCP Three-Way Handshake
The browser initiates a TCP connection to93.184.216.34on port 443 (HTTPS). A three-way handshake occurs: the client sends a SYN packet, the server responds with SYN-ACK, and the client replies with ACK. This establishes a reliable, ordered connection.TCP connection established (SYN → SYN-ACK → ACK) - 3
Step 3 — TLS Handshake (HTTPS Encryption)
Because the URL useshttps://, a TLS handshake follows. The server presents its digital certificate, the browser verifies it against trusted certificate authorities, and both sides negotiate symmetric encryption keys. All subsequent data is encrypted.Secure encrypted channel established via TLS - 4
Step 4 — HTTP GET Request
The browser sends an HTTP GET request for/index.html. This request is broken into TCP segments, each wrapped in an IP packet with source and destination addresses. Routers along the path forward each packet independently based on the destination IP address.HTTP GET /index.html sent inside encrypted TCP segments within IP packets - 5
Step 5 — Server Response & Rendering
The server processes the request and returns an HTTP response (status code 200 OK) with the HTML content in the body. The response packets travel back (possibly via a different route), are reassembled by TCP at the client, decrypted by TLS, and parsed by the browser to render the web page.Browser receives HTML, renders the page for the user
AP Exam Tip
SECTION 7
Strengths, Limitations & Security Considerations
The Internet's design choices yield tremendous strengths but also create vulnerabilities and trade-offs. Understanding both sides is essential for AP CSP questions about the benefits and harms of computing innovations, as well as questions about cybersecurity.
| Strengths | Limitations / Risks |
|---|---|
| Fault tolerance — Redundant paths mean no single point of failure can bring down the network. | Security was not built in — IP was designed for openness, not confidentiality. Protocols like TLS were added later. |
| Scalability — Hierarchical addressing and decentralized design support billions of devices. | IPv4 exhaustion — 4.3 billion addresses are insufficient; transition to IPv6 is slow and incomplete. |
| Open standards — Anyone can build devices and software that interoperate, fostering innovation. | DNS vulnerabilities — DNS spoofing and DDoS attacks on DNS servers can redirect or deny access. |
| Layered abstraction — Each layer can evolve independently (e.g., switching from copper to fiber without changing TCP). | Digital divide — Unequal access to high-speed Internet creates disparities in education, employment, and civic participation. |
| Packet switching efficiency — Bandwidth is shared dynamically, avoiding the waste of circuit-switched networks. | Privacy and surveillance — Packet metadata (IP addresses, timestamps) can be logged, enabling tracking even when content is encrypted. |
Key strengths and limitations of Internet architecture
KEY TAKEAWAY
SECTION 8
Connection to Advanced Topics
The AP CSP curriculum introduces the Internet at a conceptual level, but many of these ideas extend into more advanced topics in computer science and networking. Understanding where the AP-level content fits within the broader landscape helps contextualize exam questions and prepares you for further study.
| AP CSP Level Concept | Advanced Extension |
|---|---|
| Packets are routed through the network | Routing algorithms (Dijkstra's, BGP path selection) optimize path cost, latency, and policy constraints |
| TCP provides reliable delivery | TCP congestion control (slow start, congestion avoidance) prevents network collapse under heavy traffic |
| DNS translates names to IPs | DNSSEC adds cryptographic signatures to prevent spoofing; Content Delivery Networks (CDNs) use DNS for geographic load balancing |
| HTTPS encrypts data | Public-key cryptography, certificate chains, and the TLS 1.3 handshake involve complex mathematics (RSA, elliptic curves) |
| The Internet is a network of networks | Autonomous Systems (ASes), Internet Exchange Points (IXPs), and peering agreements define the Internet's economic and structural topology |
How AP CSP concepts map to advanced networking topics
Looking ahead, emerging technologies continue to build upon and challenge the Internet's original design. Edge computing moves processing closer to users to reduce latency. Software-defined networking (SDN) separates the control plane from the data plane, enabling programmable network management. 5G and satellite Internet expand connectivity to underserved regions. All of these innovations rely on the same foundational protocols and layered architecture you have studied in this lesson—demonstrating the enduring power of the Internet's original design principles.
SECTION 9
Practice Problems
Question 1: CONCEPTUAL
- A. Each packet is assigned a random destination IP address by the sender.
- B. Routers independently determine the best next hop for each packet based on current network conditions.
- C. The Internet Protocol reserves a dedicated circuit for each packet separately.
- D. The sending computer selects different paths for each packet before transmission.
Show answer (B)
Question 2: BASIC
shop.example.com. When a user types this domain into a browser, which system is primarily responsible for determining the IP address of the server?- A. HTTP (HyperText Transfer Protocol)
- B. TCP (Transmission Control Protocol)
- C. DNS (Domain Name System)
- D. TLS (Transport Layer Security)
Show answer (C)
Question 3: INTERMEDIATE
- A. The network can still function because redundant paths remain available for routing.
- B. All data currently being transmitted through the removed connection is permanently lost.
- C. The network's fault tolerance is reduced because there are fewer alternative paths.
- D. DNS will no longer be able to resolve domain names for devices on the network.
Show answer (A,C)
Question 4: APPLIED
3 ptsShow answer
Question 5: CRITICAL THINKING
4 ptsShow answer
SUMMARY
Lesson Summary
Summary
The Internet is a global network of networks built on packet switching, open protocols, and layered abstraction. Data is divided into packets, each carrying source and destination IP addresses, and routed independently through a mesh of routers that provide fault tolerance via redundant paths. The TCP/IP protocol suite organizes communication into four layers—Application, Transport, Internet, and Link—each handling a distinct responsibility so that technologies at one layer can evolve without disrupting others.
Key protocols include DNS (translating domain names to IP addresses), TCP (reliable, ordered delivery) and UDP (fast, best-effort delivery), and HTTP/HTTPS (web communication with optional TLS encryption). The transition from IPv4 (2³² addresses) to IPv6 (2¹²⁸ addresses) addresses the exhaustion of the original address space. While the Internet's openness enables global innovation and scalability, it also creates challenges including cybersecurity vulnerabilities, privacy concerns, and the digital divide—unequal access that limits participation in the digital economy.